# Confsec CLI
Source: https://docs.confident.security/guides/cli
The CONFSEC CLI provides a means of running prompts against the CONFSEC system using a terminal running locally.
## Installation
### Binary Download
The CONFSEC CLI binary can be downloaded directly from the [CONFSEC Web Console](https://app.confident.security/dashboard).
Click the "Clients" drop down on the top right of the Console and select the desired Operating System and binary architecture.
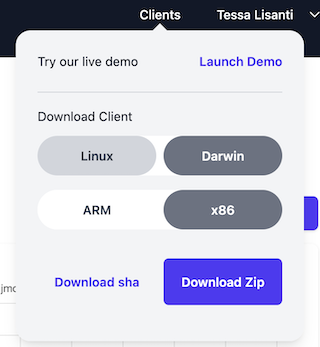 From this pane, the CONFSEC CLI binary's sha256 sum can optionally be downloaded.
This can be used to verify the CONFSEC CLI binary installation as follows, if desired:
```bash theme={null}
$ sha256sum confsec_darwin_arm64.zip
8c74d1fbf663f065cb67f4d1ec26a5d56d05f9012038f73e5a1ad7a1c63d8d18 confsec_darwin_arm64.zip
```
Once verified, the downloaded ZIP artifact can be unpacked using the `unzip` utility, e.g.:
```bash theme={null}
unzip confsec_darwin_arm64.zip
```
## Configuring CONFSEC API Keys
API Keys can be obtained from the "API Keys" tab in the CONFSEC Web Console.
Set the `API_KEY` env var to enable the CONFSEC CLI to authenticate to CONFSEC:
```bash theme={null}
export API_KEY=CONFSEC_1_
```
## Running one-shot prompts
The `confsec prompt` sub-command can be used to run single prompts against the CONFSEC system as follows:
```bash theme={null}
./confsec prompt "this is a test prompt!"
```
## Running interactive chat sessions
The `confsec prompt` sub-command can also be used to start interactive chat sessions as follows:
```bash theme={null}
./confsec prompt --interactive
```
The interactive chat mode provides the following commands to be invoked during the session:
```
Available Commands:
:q, :quit, /q, exit, quit - Exit the prompt
:h, :help, /h, ?, help - Show this help
:w, :wallet, /w - Show the contents of your wallet
:c NUMBER - Set a custom credit amount
:n COMMA SEPARATED TAGS - Set the tags of the compute nodes that can run workloads
:m MODEL_NAME - Set the default model to query
:models - Show available models
[text] - Query inference engine
```
## Running the CONFSEC Proxy
The CONFSEC CLI also supports running in a so-called "proxy" mode, in which the running
process serves as a proxy for external callers into the CONFSEC system.
```bash theme={null}
./confsec proxy
```
This sub-command is blocking, and by default creates a listener on port `21434`.
A different port can be assigned via the optional `--port` flag.
Once this command is running, requests can be forwarded to the CONFSEC system as follows:
```bash theme={null}
curl -X POST http://localhost:21434/v1/completions \
-H 'Content-Type: application/json' \
-d '{"model":"gemma3:1b","prompt":"why is the sky blue?","stream":true}'
```
The running proxy process will display some logs pertaining to the proxied requests.
## Running the Proxy UI
The Proxy UI is a TUI that provides real-time monitoring and debugging capabilities for your requests to CONFSEC system. It displays banking information, attestation status, request logs, and streaming response data in a unified dashboard.
### Starting the Proxy UI
```bash theme={null}
# Set your API key
export API_KEY="CONFSEC_1_..."
# Start the proxy UI (default port 21434)
confsec proxyui 2> proxyui.log
# Or specify custom port
confsec proxyui --port 8080 2> proxyui.log
```
### Interface Overview
The interface is divided into 6 panels arranged in 3 sections:
#### Sections
* **Banking Info**: Wallet status and credit information
* **Attestations**: Verified compute nodes and their attestation status
* **Transparency Log**: Cryptographic transparency statements
* **Request Logs**: Table showing all HTTP requests with timing and token metrics
* **Request Bodies**: Raw request content with JSON formatting
* **Response Bodies**: Streaming response content (including partial responses)
### Understanding the Data
#### Banking Information
* **Wallet Status**: Current credit balance and account state
* Updates automatically as credits are consumed
#### Attestation Panel
Shows verified compute nodes that can process your requests:
* **Node ID**: Unique identifier for each compute node
* **Tags**: Node capabilities (e.g., GPU type, model support)
* **Attestation Status**: TPM-verified security guarantees
#### Request Logs Table
Comprehensive metrics for each HTTP request:
* **Time**: Request timestamp
* **Method/Path**: HTTP details
* **Model**: AI model being queried (extracted from request body)
* **Req/Resp Size**: Data transfer amounts
* **TTFB/TTLB**: Time to first/last byte (performance metrics)
* **Tokens**: Input/output token counts and processing speed
* **Status**: HTTP response code
#### Request/Response Bodies
* **Raw Content**: Actual request and response data
* **Streaming**: Response bodies update in real-time as data arrives
* **Formatting**: JSON requests are escaped and formatted for readability
### Log Files
The proxy UI writes detailed logs to `proxyui.log` in the current directory for debugging purposes.
# Using the Web Console
Source: https://docs.confident.security/guides/web-console
## How to Create a Service Account and API Key
Head to the dashboard in the web console at [https://app.confident.security/dashboard](https://app.confident.security/dashboard) and click on the "Create Service Account" button towards the upper right hand corner of the page.
This will take you to the [API Keys page](https://app.confident.security/serviceaccounts), which lists the service accounts in your organization on the left hand side.
To add a new account, click the plus icon next to "Service Accounts".
Enter an account name and the monthly spending limit. If you don't wish to have a spending limit for the account, you can switch off the toggle next to "Monthly spending limit".
Once you've set up your service account, you can start creating API Keys to use with our confsec CLI and SDK.
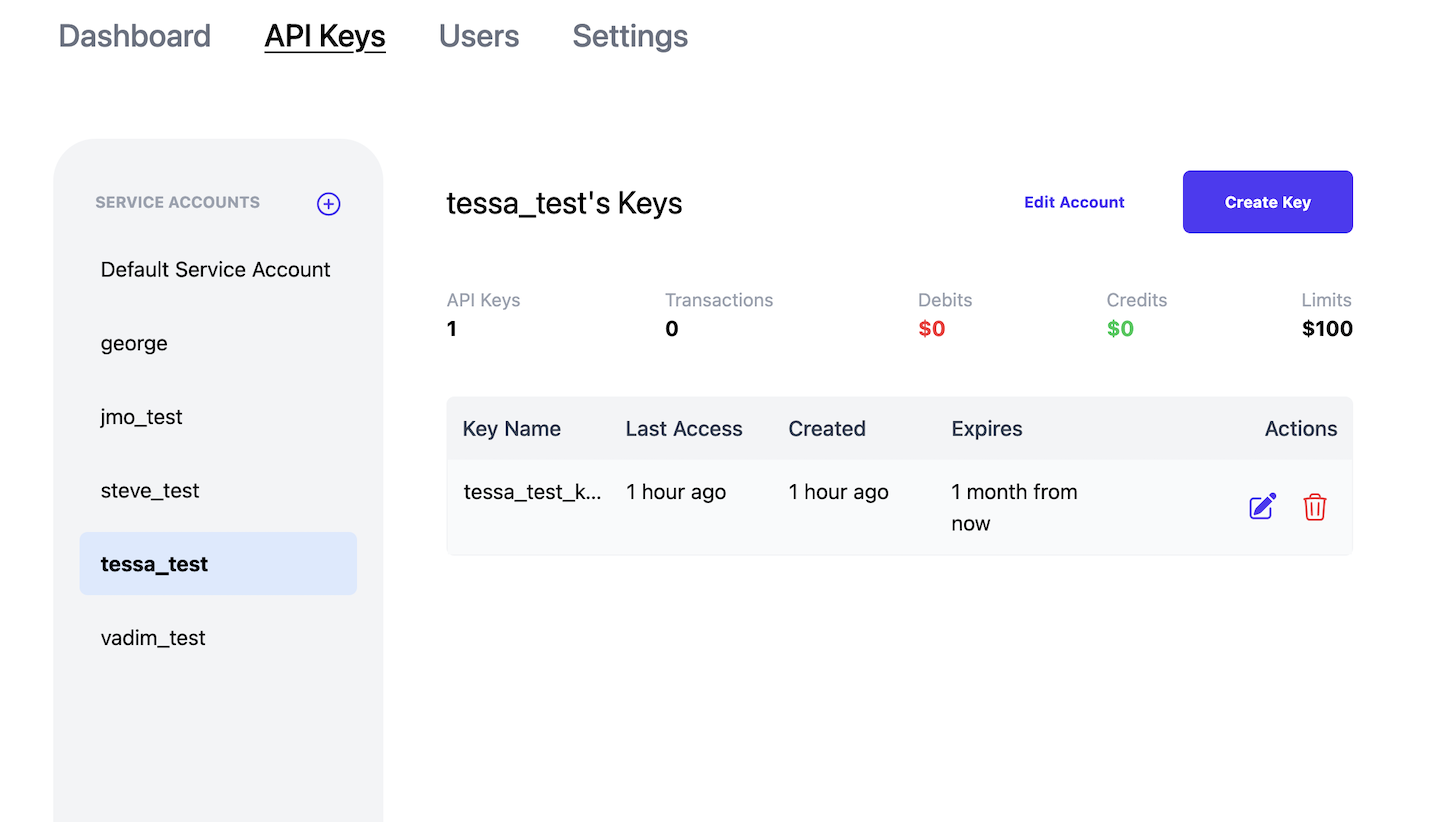
To do so, navigate to the [API Keys page](https://app.confident.security/serviceaccounts) and click on your desired service account.
There should be a "Create Key" button in the upper right corner, which will open a pop-up window for you to enter a name and expiration date for your new key.
Once you click "Create", the value of your key will be displayed like so:
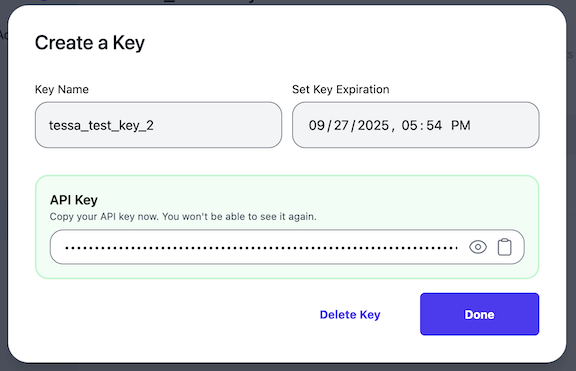 Make sure to copy your key and store it in a safe place.
Once your key is created, it will show up in your service account page, where you can edit or delete the key in the future, as shown below.
 ## Spending Limits
We support setting spending limits on both a per service account and per organization level.
You can change the spending limit that you initially set for a service account by navigating to your service account page and clicking "edit account".
This will open a pop-up where you can reset your spending limit.
To set the overall spending limit for an organization, navigate to the [Settings page](https://app.confident.security/organizations/settings), which will include an option to update your organization's spending limit.
Make sure to select the "Limited" radio button and enter the desired amount in the text box.
Remember to click "save" to have your change take effect.
Note that you must be an organization administrator or manager to update the spending limit for your organization.
## Download the Client
You can download our client directly from the website by clicking the "Clients" button in the top right of the webpage next to your profile name.
Select the operating system (Linux or Darwin (mac)) and CPU architecture (ARM or x86) of your device and click either "Download sha" or "Download zip".
## Manage Users in your organization
If you navigate to the Users page of the dashboard, you can see all of the users in your organization and their roles.
To add a user to your organization, you can click "Invite user", which will prompt you to enter the email address of the user you wish to add.
To remove a user from your organization, click the
 icon next to the user and select "Remove user" to confirm.
# Introduction
Source: https://docs.confident.security/index
CONFSEC is an enterprise-grade secure and private AI inference platform. Explore our documentation to learn how to use CONFSEC and about our privacy and security guarantees.
## Getting started
Follow our short quickstart guide.
## Guides
Learn how to use CONFSEC.
## SDKs
Develop applications using CONFSEC's easy-to-use SDKs.
# Quickstart
Source: https://docs.confident.security/quickstart
Get started with CONFSEC in just a few minutes
### Step 1: Sign in to the CONFSEC web console
### Step 2: Create a service account
1. Navigate to the **API Keys** tab from the home page
2. Click the **"+"** icon to create a new service account
3. Give the service account a name and, optionally, a spend limit
### Step 3: Create an API key
1. From your service account's detail page, click **Create Key**
2. Give the API key a name and an expiration date
3. Copy the API key and store it securely
### Step 4: Download the CONFSEC CLI
1. In the navigation bar, click **"Clients"**
2. Select the OS/architecture of your choice and download
3. Unzip the file and store the executable somewhere in your `PATH`
### Step 5: Use the CONFSEC CLI
1. Make sure your API key is set as an environment variable:
```bash
export CONFSEC_API_KEY=
```
2. Run the `confsec` executable to list available commands:
```bash
confsec --help
```
# Node.js
Source: https://docs.confident.security/sdks/node
Using the CONFSEC Node.js SDK
## Overview
The CONFSEC JavaScript/TypeScript SDK provides developers with a convenient way
to make secure and anonymous AI inference requests via CONFSEC. It can function
as a drop-in replacement for existing OpenAI clients, or as an HTTP client for
lower-level access to the CONFSEC API. Using the SDK, programs can make requests
without the need to deploy and manage the CONFSEC proxy.
## Installation
```bash theme={null}
npm install @confidentsecurity/confsec
```
## Quickstart
Use our OpenAI wrapper as a drop-in replacement for existing OpenAI clients:
```javascript theme={null}
// Use OpenAI wrapper
import { OpenAI } from '@confidentsecurity/confsec';
const client = new OpenAI({
confsecConfig: {
apiUrl: 'https://app.confident.security',
oidcIssuerRegex: 'https://token.actions.githubusercontent.com',
oidcSubjectRegex:
'^https://github.com/confidentsecurity/T/.github/workflows.*',
},
});
```
Or, for lower-level access, use the CONFSEC-enabled `fetch` implementation directly:
```javascript theme={null}
// Use fetch implementation
import { ConfsecClient } from '@confidentsecurity/confsec';
const client = new ConfsecClient({
apiKey: process.env.CONFSEC_API_KEY,
apiUrl: 'https://app.confident.security',
oidcIssuerRegex: 'https://token.actions.githubusercontent.com',
oidcSubjectRegex:
'^https://github.com/confidentsecurity/T/.github/workflows.*',
});
const confsecFetch = client.getConfsecFetch();
// Use confsecFetch for requests...
client.close();
```
## Configuration
We aim to make the SDK as config-free as possible. However, there are some
parameters you can optionally configure to control how the client interacts
with the CONFSEC backend:
* `apiUrl (string)`: The URL for the service implementing the OpenPCC auth API.
* `identityPolicySource (number)`: Accepts values from the `IdentityPolicySource`
enum. Controls the source of the identity policy that the client uses to
validate the signing identity of artifacts in the OpenPCC transparency log. By
default `IdentityPolicySource.CONFIGURED` is used, which requires the caller
to configure at least one of `oidcIssuer` or `oidcIssuerRegex`, and at least
one of `oidcSubject` or `oidcSubjectRegex`. Alternatively, the caller could set
this as `IdentityPolicySource.UNSAFE_REMOTE`, which allows the client to
receive and trust the identity policy from the auth server. This is unsafe and
should only be used in development environments.
* `oidcIssuer (string)`: The OIDC issuer to trust for OpenPCC transparency log
artifacts.
* `oidcIssuerRegex (string)`: A regular expression matching the OIDC issuers to
trust for OpenPCC transparency log artifacts. Can be used in place of
`oidcIssuer` to trust multiple issuers.
* `oidcSubject (string)`: The OIDC subject to trust for OpenPCC transparency log
artifacts.
* `oidcSubjectRegex (string)`: A regular expression matching the OIDC subjects to
trust for OpenPCC transparency log artifacts. Can be used in place of
`oidcSubject` to trust multiple subjects.
* `concurrentRequestsTarget (number)`: Allows the client to specify the desired
request parallelism. This primarily impacts the number of credits that the
client will maintain cached and available to use immediately. Higher values
for this parameter will increase the maximum request throughput that the
client can achieve, but also increases the amount of credits that may be lost
permanently if the client process terminates without properly closing the
client.
* `defaultNodeTags (string[])`: Allows the client to specify default filters
for CONFSEC compute nodes that will be applied to all requests. Users should
not need to configure this in most cases, especially when using the OpenAI
wrapper, since the `model` field of any request will be automatically mapped
to the appropriate CONFSEC node tags.
## Usage
### OpenAI Wrapper
The `OpenAI` class can be initialized explicitly with an API key, by passing the
`apiKey` parameter to the constructor. Otherwise, it will attempt to load the
API key from the `CONFSEC_API_KEY` environment variable.
It is very important to call `client.close()` when you are done with the client
to ensure that all resources are properly released. This can be done explicitly,
or by using the client in a try/finally block. Failure to do so may result
in credits being lost.
Currently, the following subset of APIs are supported:
* Completions
* Chat
```javascript theme={null}
import { OpenAI } from '@confidentsecurity/confsec';
const client = new OpenAI({
confsecConfig: {
apiUrl: 'https://app.confident.security',
oidcIssuerRegex: 'https://token.actions.githubusercontent.com',
oidcSubjectRegex:
'^https://github.com/confidentsecurity/T/.github/workflows.*',
},
});
try {
const stream = await client.chat.completions.create({
model: 'gemma3:1b',
messages: [
{
role: 'user',
content: 'What is the meaning of life?',
},
],
stream: true,
});
for await (const chunk of stream) {
process.stdout.write(chunk.choices[0]?.delta?.content || '');
}
} finally {
client.close();
}
```
### `fetch` Implementation
The `ConfsecClient` class can also be initialized explicitly for lower-level
access to the CONFSEC API. It's recommended to get a fetch function using the
`getConfsecFetch` method of the `ConfsecClient` class which will use the client
as the transport, instead of calling `ConfsecClient`'s methods directly. This
function returns a function which can be used as a drop-in replacement for the
global `fetch` function.
As with the `OpenAI` class, it is very important to call `client.close()` when
you are done with the client to ensure that all resources are properly released.
This should be done explicitly in a try/finally block. Failure to do so may
result in credits being lost.
```javascript theme={null}
import { ConfsecClient } from '@confidentsecurity/confsec';
const client = new ConfsecClient({
apiKey: process.env.CONFSEC_API_KEY,
apiUrl: 'https://app.confident.security',
oidcIssuerRegex: 'https://token.actions.githubusercontent.com',
oidcSubjectRegex:
'^https://github.com/confidentsecurity/T/.github/workflows.*',
});
try {
const confsecFetch = client.getConfsecFetch();
const response = await confsecFetch(
// Important: the base URL must be set to "https://confsec.invalid"
'https://confsec.invalid/v1/chat/completions',
{
method: 'POST',
headers: {
'Content-Type': 'application/json',
},
body: JSON.stringify({
model: 'gemma3:1b',
messages: [{ role: 'user', content: 'What is the meaning of life?' }],
}),
}
);
const data = await response.json();
console.log(data);
} finally {
client.close();
}
```
## License
This package is licensed under the Confident Security Limited License. See [LICENSE](./LICENSE) for details.
# Python
Source: https://docs.confident.security/sdks/python
Using the CONFSEC Python SDK
## Overview
The CONFSEC Python SDK provides developers with a convenient way to make secure
and anonymous AI inference requests via CONFSEC. It can function as a drop-in
replacement for existing OpenAI clients, or as an HTTP client for lower-level
access to the CONFSEC API. Using the SDK, programs can make requests without the
need to deploy and manager the CONFSEC proxy.
## Installation
```bash theme={null}
pip install confsec
```
## Quickstart
Use our OpenAI wrapper as a drop-in replacement for existing OpenAI clients:
```python theme={null}
# Use OpenAI wrapper
from confsec.openai import OpenAI
client = OpenAI(confsec_config={
"api_url": "https://app.confident.security",
"oidc_issuer": "https://token.actions.githubusercontent.com",
"oidc_subject": "^https://github.com/confidentsecurity/T/.github/workflows.*",
})
```
Or, for lower-level access, use the CONFSEC-enabled HTTP client directly:
```python theme={null}
# Use HTTP client
import os
from confsec import ConfsecClient
with ConfsecClient(
api_url="https://app.confident.security",
api_key=os.environ["CONFSEC_API_KEY"],
oidc_issuer="https://token.actions.githubusercontent.com",
oidc_subject="^https://github.com/confidentsecurity/T/.github/workflows.*",
) as client:
http = client.get_http_client()
```
## Configuration
We aim to make the SDK as config-free as possible. However, there are some
parameters you can optionally configure to control how the client interacts
with the CONFSEC backend:
* `api_url (str)`: The URL for the service implementing the OpenPCC auth API.
* `identity_policy_source (int)`: Accepts values from the `IdentityPolicySource`
enum. Controls the source of the identity policy that the client uses to
validate the signing identity of artifacts in the OpenPCC transparency log. By
default `IdentityPolicySource.CONFIGURED` is used, which requires the caller
to configure at least one of `oidc_issuer` or `oidc_issuer_regex`, and at least
one of `oidc_subject` or `oidc_subject_regex`. Alternatively, the caller could set
this as `IdentityPolicySource.UNSAFE_REMOTE`, which allows the client to
receive and trust the identity policy from the auth server. This is unsafe and
should only be used in development environments.
* `oidc_issuer (str)`: The OIDC issuer to trust for OpenPCC transparency log
artifacts.
* `oidc_issuer_regex (str)`: A regular expression matching the OIDC issuers to
trust for OpenPCC transparency log artifacts. Can be used in place of
`oidc_issuer` to trust multiple issuers.
* `oidc_subject (str)`: The OIDC subject to trust for OpenPCC transparency log
artifacts.
* `oidcSubject_Regex (str)`: A regular expression matching the OIDC subjects to
trust for OpenPCC transparency log artifacts. Can be used in place of
`oidc_subject` to trust multiple subjects.
* `concurrent_requests_target (int)`: Allows the client to specify the desired
request parallelism. This primarily impacts the number of credits that the
client will maintain cached and available to use immediately. Higher values
for this parameter will increase the maximum request throughput that the
client can achieve, but also increases the amount of credits that may be lost
permanently if the client process terminates without properly closing the
client.
* `default_node_tags (list[str])`: Allows the client to specify default filters
for CONFSEC compute nodes that will be applied to all requests. Users should
not need to configure this in most cases, especially when using the OpenAI
wrapper, since the `model` field of any request will be automatically mapped
to the appropriate CONFSEC node tags.
## Usage
### OpenAI Wrapper
The `OpenAI` class can be initialized explicitly with an API key, by passing the
`api_key` parameter to the constructor. Otherwise, it will attempt to load the
API key from the `CONFSEC_API_KEY` environment variable.
It is very important to call `client.close()` when you are done with the client
to ensure that all resources are properly released. This can be done explicitly,
or by using the `OpenAI` class as a context manager. Failure to do so may result
in credits being lost.
Currently, the following subset of APIs are supported:
* Completions
* Chat
```python theme={null}
import os
client = OpenAI(confsec_config={
"api_url": "https://app.confident.security",
"oidc_issuer": "https://token.actions.githubusercontent.com",
"oidc_subject": "^https://github.com/confidentsecurity/T/.github/workflows.*",
})
stream = client.chat.completions.create(
model="gemma3:1b",
messages=[
{
"role": "user",
"content": "What is the meaning of life?",
}
],
stream=True,
)
for chunk in stream:
print(chunk.choices[0].delta.content, end="")
client.close()
```
For async usage, use the `AsyncOpenAI` class:
```python theme={null}
from confsec.openai import AsyncOpenAI
async def main():
client = AsyncOpenAI(confsec_config={
"api_url": "https://app.confident.security",
"oidc_issuer_regex": "https://token.actions.githubusercontent.com",
"oidc_subject_regex": "^https://github.com/confidentsecurity/T/.github/workflows.*",
})
stream = await client.chat.completions.create(
model="gemma3:1b",
messages=[{"role": "user", "content": "What is the meaning of life?"}],
stream=True,
)
async for chunk in stream:
print(chunk.choices[0].delta.content, end="")
client.close()
```
### HTTP Client
The `ConfsecClient` class can also be initialized explicitly for lower-level
access to the CONFSEC API. It's recommended to create an HTTP client using the
`get_http_client` method of the `ConfsecClient` class which will use the client
as the transport, instead of calling `ConfsecClient`'s methods directly.
As with the `OpenAI` class, it is very important to call `client.close()` when
you are done with the client to ensure that all resources are properly released.
This can be done explicitly, or by using the `ConfsecClient` class as a context
manager. Failure to do so may result in credits being lost.
```python theme={null}
import os
from confsec import ConfsecClient
with ConfsecClient(
api_url="https://app.confident.security",
api_key=os.environ["CONFSEC_API_KEY"],
oidc_issuer="https://token.actions.githubusercontent.com",
oidc_subject="^https://github.com/confidentsecurity/T/.github/workflows.*",
) as client:
http = client.get_http_client()
response = http.request(
"POST",
# Important: the base URL must be set to "https://confsec.invalid"
"https://confsec.invalid/v1/chat/completions",
json={
"model": "gemma3:1b",
"messages": [
{"role": "user", "content": "What is the meaning of life?"}
]
}
)
print(response.json())
```
For async usage, use `get_async_http_client`:
```python theme={null}
import os
from confsec import ConfsecClient
async def main():
with ConfsecClient(
api_url="https://app.confident.security",
api_key=os.environ["CONFSEC_API_KEY"],
oidc_issuer_regex="https://token.actions.githubusercontent.com",
oidc_subject_regex="^https://github.com/confidentsecurity/T/.github/workflows.*",
) as client:
http = client.get_async_http_client()
response = await http.request(
"POST",
"https://confsec.invalid/v1/chat/completions",
json={
"model": "gemma3:1b",
"messages": [
{"role": "user", "content": "What is the meaning of life?"}
]
}
)
print(response.json())
```